The reported 2025 and July 2026 incidents concerned public shared snapshots becoming unexpectedly searchable. The reporting does not establish unauthorized access to unshared private chats. A public link already lets someone view its snapshot; search results make that material easier to discover. The route by which every indexed link reached a search engine remains unresolved.
Incident scope at a glance
- Risk level: High
- Evidence level: High
- Reported exposure: Public shared snapshots appearing in search, including sensitive information in visible text and artifacts
- Scope limit: These reports do not demonstrate access to unshared chats. Current documentation excludes later messages unless the snapshot is updated, attached files themselves and raw MCP tool-call data; excerpts or summaries in visible responses can still expose source information. Team and Enterprise sharing is documented as organization-restricted.
- Dated remediation observation: July 27–28 reporting described Google-result disappearance. That is a historical search observation, not a current check or proof that other engines, references, screenshots or third-party copies disappeared.
- Scale: Unresolved. No reliable total for the July 2026 event has been independently established.
Anthropic’s sharing documentation describes private-by-default chats and explicit snapshot creation. Review everything included before creating a link, including answers derived from private files or tools.
This is a technical incident-response guide, not legal advice.
Current documented policy, checked October 3, 2026
Anthropic’s public-link guidance says Free, Pro and Max public links are view-only snapshots accessible without a Claude account. It says shared pages carry noindex and Anthropic publishes no shared-chat directory or sitemap. Those are current provider statements, not our measurement of valid snapshot headers or evidence of the configuration in 2025 or July 2026.
A noindex instruction asks search engines to omit a page; it does not restrict who can open it or copy it. A privately sent public link can be forwarded. Turning sharing off disables the provider-hosted link, while screenshots, archives and other copies can remain. Team and Enterprise links require signed-in members of the same organization, according to the same guidance.
Timeline: September 2025 and July 2026
| Date | What was established |
|---|---|
| September 8, 2025 | Forbes reported searchable shared Claude transcripts and subsequent Google-result disappearance. Its search estimate was not an audited affected total. |
| September 8, 2025 | Anthropic told Forbes that users’ online link posts explained discovery. Forbes also interviewed a user who denied posting their link. Neither statement establishes how every URL was discovered. |
| July 25, 2026 | TechCrunch dated the Reddit discovery to this Saturday; AIHackers did not reproduce it. |
| July 27, 2026 | WIRED reported searchable shared snapshots, missing HTML noindex tags in its sample, and Google-result disappearance while Bing results remained. That sample does not establish every page’s headers. |
| July 28, 2026 | WIRED added Anthropic’s explanation that public link posting enabled discovery and it supplied no directory or sitemap. This is attributed provider testimony, not a proven root cause. |
TechCrunch’s July report provides additional contemporary coverage. We did not open strangers’ snapshots or search for exposed credentials during this review.
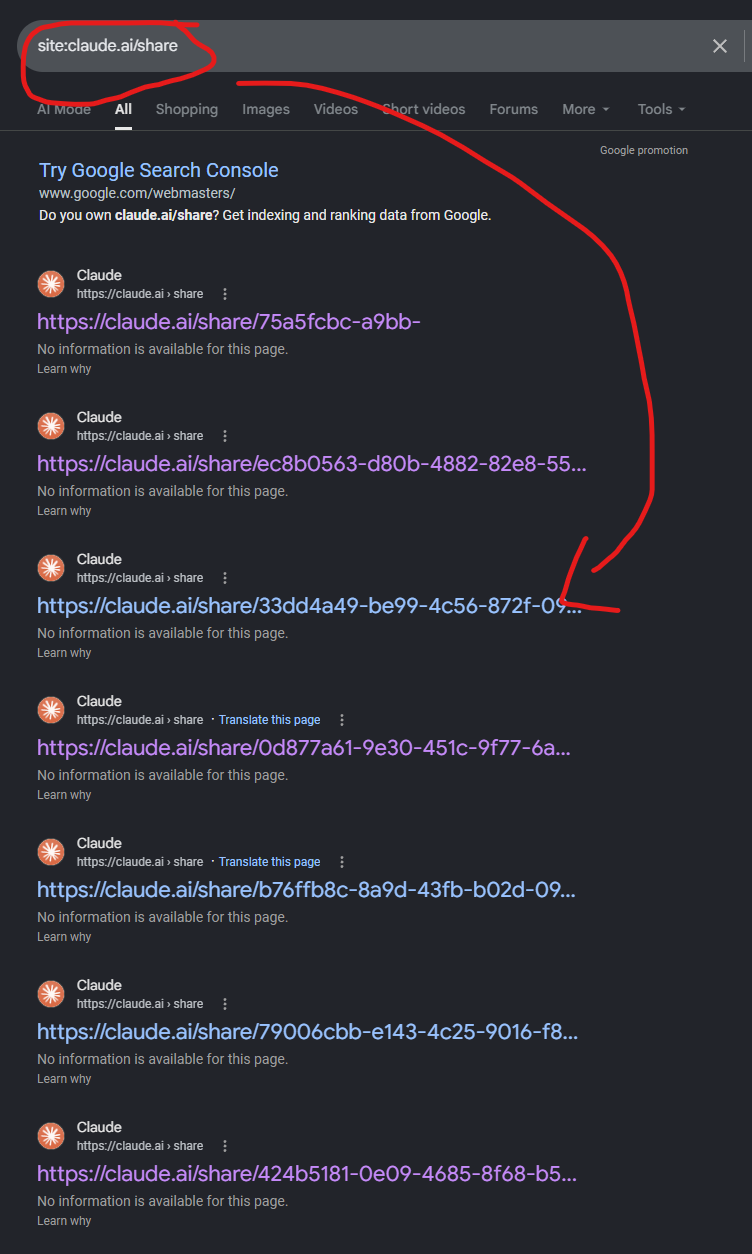
Do not use the screenshot to estimate how many snapshots existed or remain indexed. It records no capture date, exposes no conversation content, and does not establish present search behavior.
Evidence matrix
| Evidence class | What it supports | What it does not support |
|---|---|---|
| Anthropic documentation | Current snapshot/access, noindex, no-directory/sitemap and unshare policies | Historical implementation, crawler compliance, indexed totals or erasure of third-party copies |
| Independent reporting | Searchable public snapshots in September 2025 and July 2026; reporters’ dated observations; attributed provider explanations | A complete inventory, a confirmed cause for every link or proof that every copy disappeared |
| AIHackers historical check | On August 24 at 15:21 SGT, one nonexistent all-zero share UUID returned 200 text/html and literal X-Robots-Tag: none to normal, Googlebot and Bingbot user-agent strings; the fetched robots.txt did not disallow /share/. This is the retained historical record, not a new test. | Behavior of any real snapshot, historical headers on valid snapshots, verified crawler identity, current search results or universal remediation |
| Reader-supplied screenshot | An undated image of search results showing share URLs | Chat contents, capture date, complete scale or present discoverability |
| Unresolved | Discovery path for each link, valid-snapshot header history, July scale and remaining copies | Any precise affected-count or root-cause claim |
The evidence label supports the reported exposure and documented controls. It does not certify a root cause, unresolved scale or universal remediation. The nonexistent-route check cannot validate snapshot behavior.
Public access and search discovery are separate
A public snapshot and its discovery are separate events. One possible path is:
- Explicit share action: A user created a public snapshot.
- Anonymous public access: Anyone holding the URL could view it without joining the owner’s account.
- Link discovery: A crawler found a reference to the URL. Public posting is Anthropic’s explanation; the reports do not prove that route for every snapshot.
- Indexing or copying: A search engine listed the URL, or someone saved content independently of the provider’s search instructions.
An unguessable URL reduces accidental guessing; it does not authenticate recipients. Anyone who receives a public link can forward it or copy its contents.
Why robots.txt and noindex can conflict
robots.txt controls crawler access; a page-level noindex directive controls whether a fetched page should appear in results. They are not interchangeable.
Google’s documentation warns that robots meta tags and X-Robots-Tag headers are discovered only when a URL is crawled. If robots.txt blocks that fetch, the crawler cannot see the page’s noindex instruction. Bing documents its supported robots directives.
Google treats X-Robots-Tag: none as noindex, nofollow. A crawl block can prevent a crawler from seeing that indexing directive, but this general interaction does not prove the historical cause here. The August 24 response tested a nonexistent route and says nothing about headers on valid snapshots before or after that check.
What to do now
1. Inventory and unshare every sensitive snapshot
Open Settings → Privacy → Shared chats, review the title, sharing date, and link for every entry, then select Unshare for anything that should not remain public. Anthropic says this changes the snapshot from Public to Private and disables the direct link.
Record the sharing time, unshare time, affected systems, and response owner in your private incident log. Do not paste exposed material into a public ticket.
2. Revoke secrets before chasing search results
Treat every credential visible in a public snapshot as compromised. GitHub’s secret-remediation guidance prioritizes immediate revocation for active public or production secrets.
- Revoke or rotate the secret at its issuer.
- Replace it in every application, workflow, device, and dependency that used it.
- Terminate sessions or tokens derived from it.
- Audit activity from the original sharing time onward.
- Only then remove stale copies and references.
Deleting a chat, unsharing a snapshot, or deindexing a result does not make an exposed credential safe again.
3. Replace keys and wallets, not just strings
Handle SSH and signing-key exposure as a new-keypair event: generate a fresh pair, deploy the new public key, remove trust for the old key everywhere, revoke certificates where applicable, and review signed or authenticated activity.
If a cryptocurrency seed phrase or private key appeared, create a new wallet from uncompromised material and move assets. Removing the page cannot restore secrecy to the old key.
4. Escalate regulated or organizational data
Personal, medical, customer, employee, child, legal, or company-confidential data belongs in the organization’s security and privacy process. Preserve a minimal private timeline, notify the responsible incident lead or data-protection contact, and follow contractual or regulatory procedures. Do not contact people named in reporting or copy their exposed data into a new system.
5. Request search removal after source revocation
After unsharing and rotating secrets, use Google’s outdated-content refresh for a removed or materially changed page. Personal-information removal has separate eligibility rules. Microsoft provides routes to remove cached pages or request Bing content removal.
Search removal affects a search surface, not the rest of the internet. Google explicitly warns that removed results can remain reachable through direct links, social media, or other engines. Neither request erases screenshots, private archives, downloads, or third-party copies.
How to prevent a repeat
- Treat every public share link as publication. “Anyone with the link” is not a private audience once the link leaves a controlled channel.
- Create a new redacted transcript for sharing. Do not publish the working chat and hope reviewers notice its earlier context.
- Scan before sharing. Check prompts, outputs, code, terminal logs, artifacts, names, contact details, customer data, credentials, private URLs, and system identifiers.
- Prefer organization-restricted sharing. Use a managed Team or Enterprise boundary when recipients belong to the same organization and its controls fit the data.
- Make policy explicit. Prohibit public sharing of sensitive chats in team rules, code-review checklists, and agent instructions. Keep the rule in the team’s current security guidance and review process.
- Test revocation. A control is incomplete if owners cannot inventory and disable links quickly during an incident.
The same publication rule applies outside Claude. OpenCode session sharing also creates a public link and moves conversation history to a hosted service.
Five controls that must stay separate
Retention, deletion, training, public-link access, and search indexing answer different questions:
| Control | Question |
|---|---|
| Retention | How long does a provider or connected system keep data? |
| Deletion | What copy is removed, on what schedule, and with which exceptions? |
| Training | May the provider use content to improve models? |
| Public-link access | Can someone holding a URL retrieve a snapshot? |
| Search indexing | Can a search engine make that URL easy to discover? |
Turning off training does not revoke a public link. Deleting account history does not rotate a leaked key. Removing a search result does not erase a third-party copy. The Claude vs OpenAI retention explainer maps the adjacent storage and deletion controls.
What local models remove—and what they do not
A local model removes this specific provider-hosted share-link path only when the complete workflow stays local: inference, UI, history, RAG or vector storage, telemetry, backups, and tools. A local runtime with a cloud-synced UI, remote MCP server, hosted search tool, shared GPU service, or off-device backup still crosses another data boundary.
Use the Local LLM guide to choose that lane for the right reason. “Local inference” alone is not a blanket privacy guarantee.
Sources and archive status
- Anthropic: Public links for shared chats — current guidance checked October 3, 2026; archive-pending
- Forbes: September 8, 2025 reporting — checked October 3, 2026; archive-pending
- Anthropic: Share and unshare chats (Archive)
- Anthropic: Consumer Terms of Service (Archive)
- WIRED: Private Claude Chats Exposed in Google and Bing Search Results (Archive)
- TechCrunch: PSA: Your Claude shared chats and Artifacts may have ended up on Google (Archive)
- Google Search Central: Robots meta tags specifications (Archive)
- Bing Webmaster Tools: Supported robots meta tags and attributes (Archive)
- GitHub: Remediating a leaked secret (Archive)
- Google Search Help: Remove private information (Archive)
- Google Search Help: Refresh outdated content — checked October 3, 2026; archive-pending
- Microsoft Support: How Bing delivers search results (Archive)
Historical archive record: the original nine captures were recorded as replaying 200 text/html on August 20, 2026; that replay was not repeated for this correction. The August 24 route check did not fetch or archive any real shared chat. Current documentation and incident reports were reopened October 3, 2026.
Related guidance
- Claude terms overview
- Risk level rubric
- Claude vs OpenAI data retention
- Running LLMs locally
- OpenCode sharing and privacy
- Risks index
Documentation and reporting reviewed October 3, 2026. The route-header observation remains dated August 24; current valid-snapshot headers and search results were not tested. Controls and provider documentation can change independently.